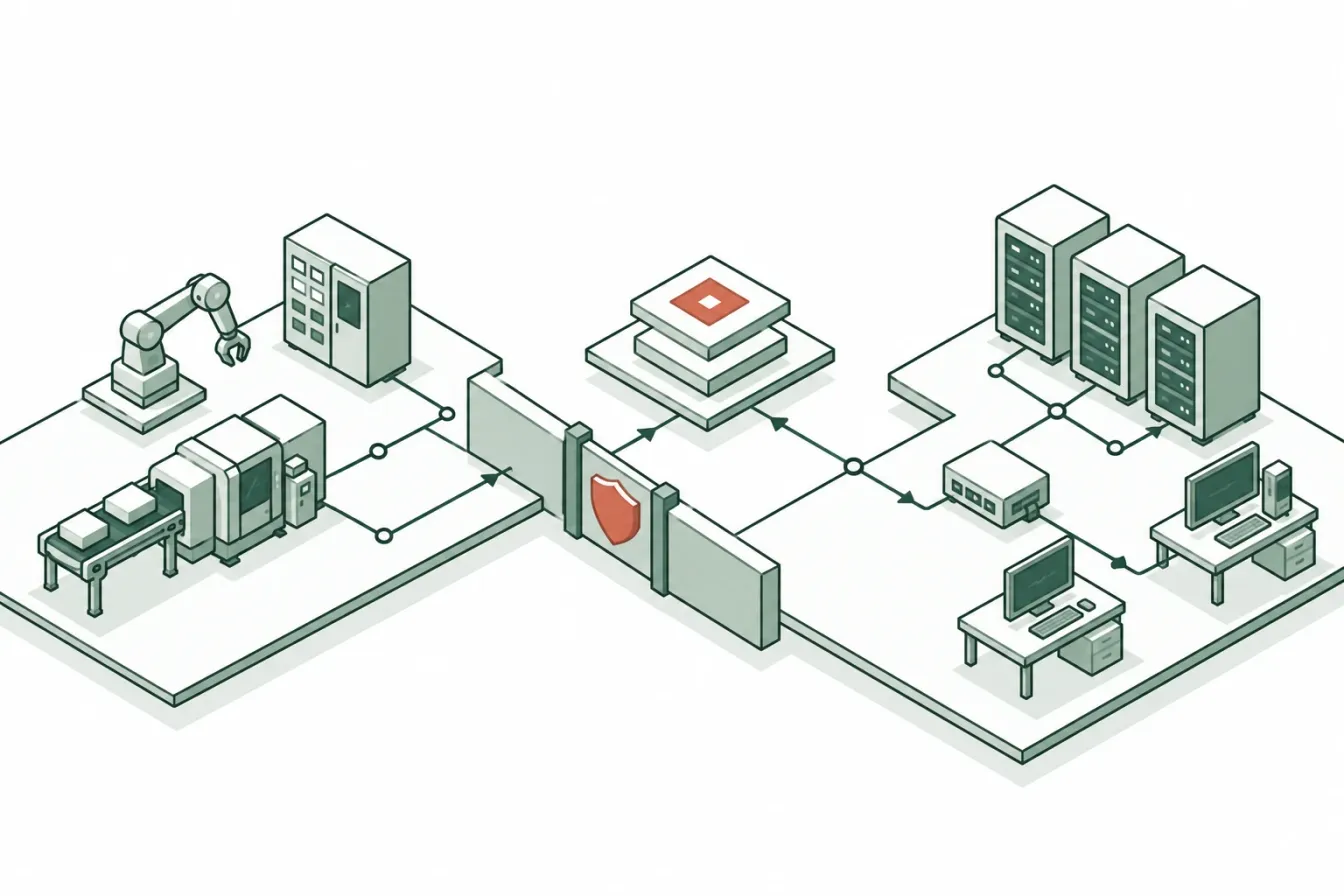
The Great IT vs. OT Divide
For decades, Information Technology (IT) and Operational Technology (OT) have existed in parallel universes. IT lives in temperature-controlled server rooms, dealing with enterprise systems like SAP, Apache Kafka, and AWS. They prioritize data accessibility, rapid iterations, and large scale.
OT, on the other hand, lives on the roaring, gritty factory floor. Their world revolves around PLCs, robotics, SCADA systems, and high-voltage machinery. They prioritize one thing above all else: High Reliability and Physical Safety.
Today, "Industry 4.0" demands that these two departments merge-a concept known as IT/OT Convergence. Management wants to stream real-time PLC counts into the cloud ERP to predict supply chain shortages. However, when the IT department asks OT to "just open a firewall port to the Siemens PLC," the OT team flatly refuses, citing massive cybersecurity risks. And they are right. The right answer is a governed IT/OT integration layer, not another fragile point connection.
So, how do you bridge the gap?
- DMZ: Secure IT/OT demilitarized zone
- Governed: Approved OT → IT data paths
Observed performance depends on workload shape, node capacity, and deployment design.
The scaling limit of point-to-point integration
The historical approach to IT/OT integration was point-to-point. If the Quality team needed SPC (Statistical Process Control) data, a custom script was written to bridge the PLC directly to the quality database. If Finance needed energy consumption data, another script was strung from the smart meter directly to the ERP.
This creates an unmaintainable "spaghetti architecture". It is fragile, difficult to scale across multiple factories, and in many deployments it leads to multiple inbound firewall exceptions.
A shared model: Unified Namespace (UNS)
The modern approach to convergence relies on a Unified Namespace (UNS). A UNS acts as a single, centralized message broker (typically MQTT-based) that represents the current state of your entire business.
Instead of writing custom scripts for every application, the OT side publishes data to the UNS in a standardized format. The IT side then subscribes to the UNS to consume that data.
Why does this matter? It creates a clean decoupling of systems. The SAP ERP doesn't need to know the IP address of a robot on the floor, and the robot doesn't care if the ERP goes down for maintenance. They both only talk to the central UNS.
S7-1500 → Secure Gateway: OPC UA
Modbus TCP → Secure Gateway: Modbus
Secure Gateway → MQTT Central Hub: Outbound TLS
MQTT Central Hub → Business Logic: Subscribes
MQTT Central Hub → Data Lake: Subscribes
Solving Security Risk: "Outbound-Only" Architecture
Even with a UNS, the physical mechanism of extracting data from a PLC typically should be flawless. You cannot expose an industrial control network (Level 1/2 of the Purdue Model) to the internet.
This is where the Proxus IT/OT Bridge relies on strict Outbound-Only architectural principles to keep the factory safe:
- No Inbound Ports: The Proxus Edge Gateway sits on the factory floor. It reaches out into the OT network via industrial protocols (like OPC UA or Modbus) to read data.
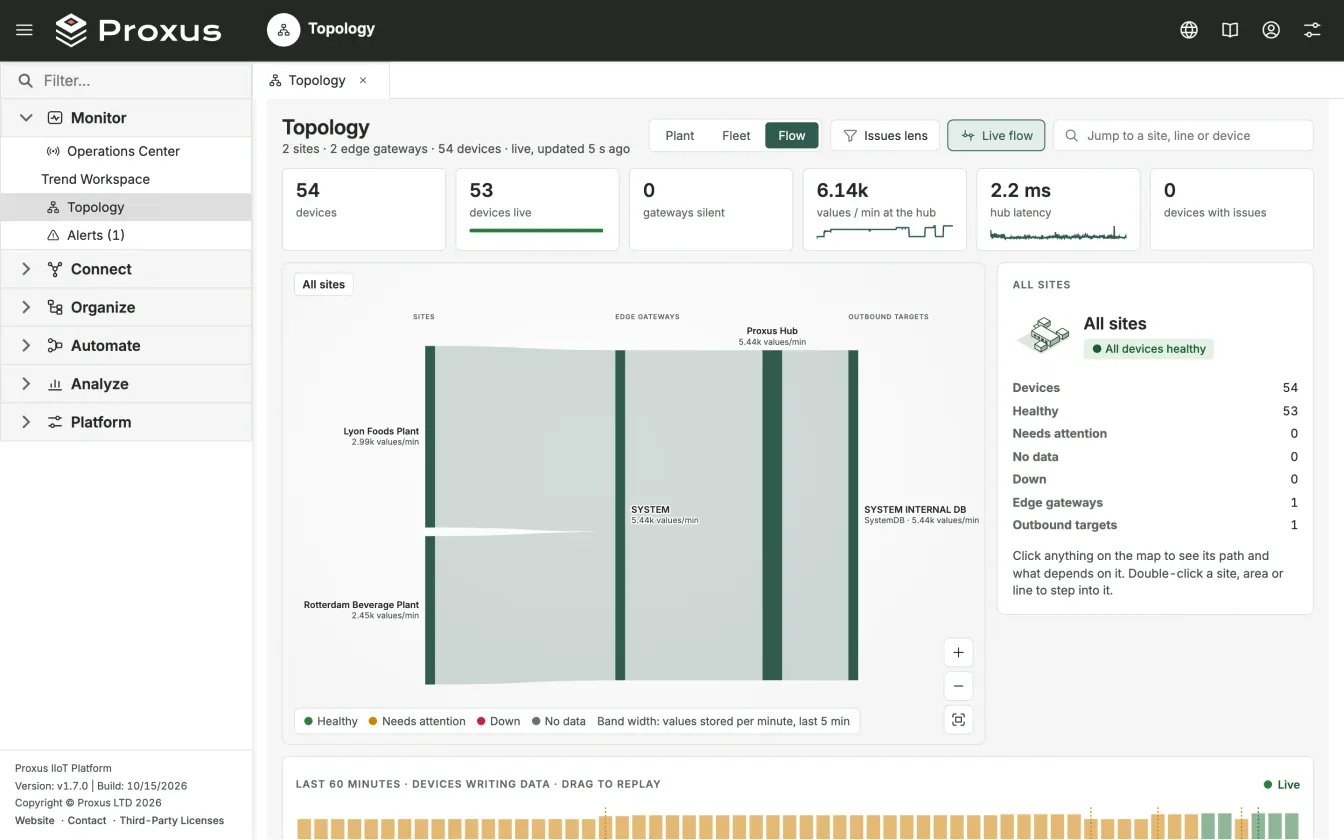
- Streaming "Up": The edge gateway initiates an outbound TLS connection to the central platform, verified against the platform's certificate authority, and identifies itself with its own revocable credential. Firewall, proxy, DNS, and destination controls remain part of the deployment design; Security and deployment covers transport encryption and certificates.
- Separate writeback boundary: Telemetry export must not imply command authority. Any inbound command path requires separate identity, authorization, validation, audit, timeout, network, and safety controls.
Data Normalization: Speaking the Same Language
Even if the pipeline is secure, raw OT data is often useless to IT. A PLC might output a tag named DB40.DBD12 which means nothing to a cloud developer.
A true IT/OT Convergence platform typically should translate this raw signal. Before Proxus routes data to enterprise targets, it Normalizes the Tags. It transforms DB40.DBD12 into a clean, contextualized payload like SiteA / Line1 / Press_Machine / Temperature_C. That same normalized context can then feed an industrial data platform instead of being trapped in one custom export.
When the IT systems (like a Data Lake or AI platform) receive this data, it is already clean, structured, and ready for analytics. The integrations list shows the brokers, databases and cloud services Proxus delivers to, Apache Kafka, Azure and AWS among them.
Conclusion
True IT/OT Convergence isn't just about stringing cables between the factory network and the corporate cloud. It is about building a secure, governed bridge that respects the priorities of both departments.
By utilizing a Unified Namespace, enforcing Outbound-Only network policies, and automatically Normalizing Data, organizations can improve data availability for Enterprise systems while preserving stronger Shop Floor security boundaries.
When this may not be suitable
- Lower-frequency telemetry may not justify full distributed complexity.
- Small single-line plants may prefer simpler architectures first.
- Strict legacy constraints may require phased adoption.
- Safety-critical closed-loop control should remain in PLC/Safety PLC layers.
Outcomes depend on workload profile, hardware capacity, and deployment topology.
Frequently Asked Questions
What does "outbound-only" mean in IT/OT convergence?
The Edge Gateway initiates all connections outward from the OT network to the IT/cloud layer. No inbound ports are opened on the factory firewall. This significantly constrains direct reverse traversal from IT/cloud into OT, but does not replace credential hygiene, segmentation, and monitoring controls. It is a foundational network-security pattern in industrial IoT.
Who should own the IT/OT bridge - IT or OT?
Neither exclusively. Best practice is a cross-functional team with OT owning the edge configuration (protocols, tag mapping) and IT owning the cloud infrastructure (broker, data lake, IAM). The Unified Namespace serves as the shared contract between both teams.
How does data normalization work at the edge?
Raw PLC addresses (e.g., DB40.DBD12) are mapped to semantic topic paths (e.g., SiteA/Line1/Press/Temperature_C) with engineering unit conversion, timestamp enrichment, and data type standardization. This happens inside the Edge Gateway before data leaves the OT network - see OT DataOps for the full pipeline.
References
- IEC 62443 - Industrial cybersecurity framework defining security zones and conduits for IT/OT network segmentation.
- ISA-95 / IEC 62264 - Defines the functional hierarchy (Levels 0–4) that the IT/OT bridge spans.
- NIST SP 800-82 - Guide to Industrial Control Systems Security, foundational for OT network protection strategies.
Last updated August 6, 2026